
Badly dressed
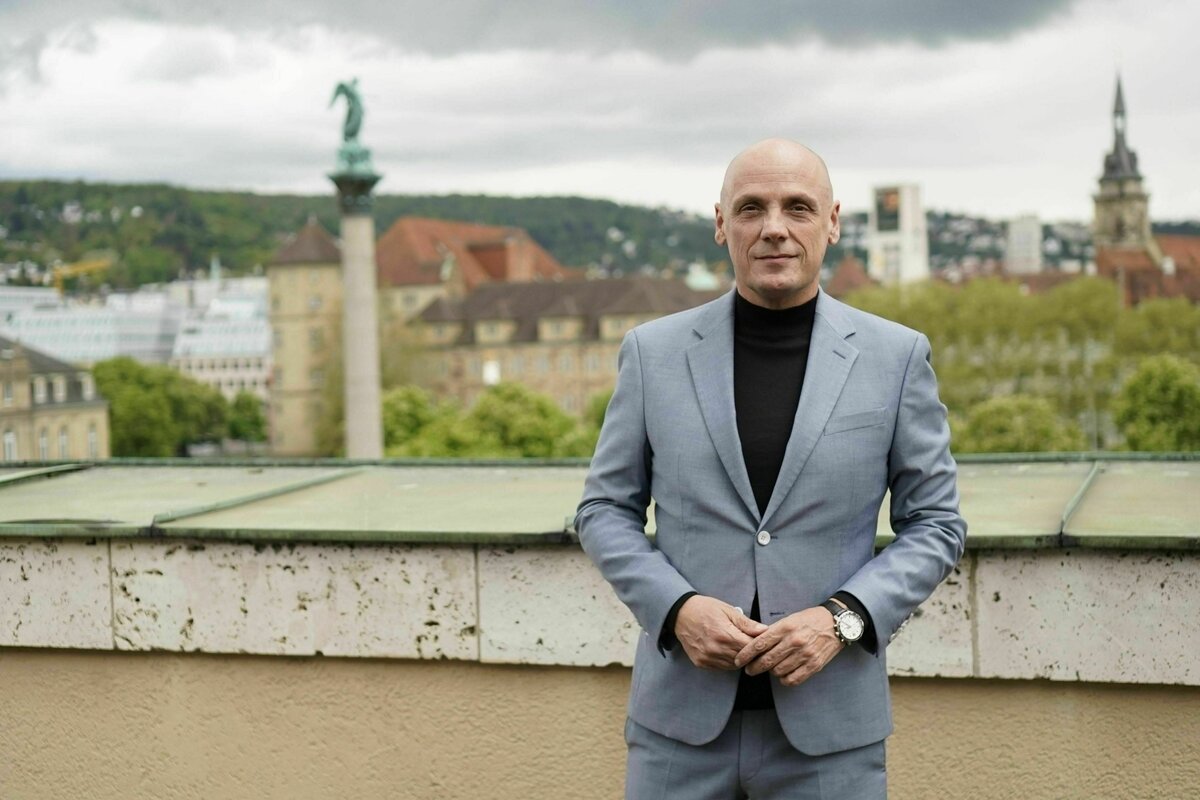
Image of a guy in a plain shirt
The ads of the accessory industrial complex have gotten quite subversive.
Edit: Also the guy looks very snuggleable
Hi!
My previous/alt account is yetAnotherUser@feddit.de which will be abandoned soon.
Badly dressed
Image of a guy in a plain shirt
The ads of the accessory industrial complex have gotten quite subversive.
Edit: Also the guy looks very snuggleable
Means it’s summer and you don’t have air conditioning.
Source: Did not wear a shirt at home for the last two months.
I think this is UK traffic sign 955 (Route for use by pedal cycles only):

Ich mochte die Antwortmöglichkeiten, bei denen man immer ein großes Arschloch sein konnte. Wie z.B.:
https://www.fahrschule.de/Fragenkatalog/1.1.02-029
Eine Person im Rollstuhl schafft es nach dem Überqueren der Straße nicht, mit dem Rollstuhl den Bordstein zu überwinden, um den Gehweg zu erreichen. Wie verhalten Sie sich?
[ ✔ ] Ich hupe und fahre um die Person herum

Young people too are increasingly requesting assisted suicide. I read an article about how in 2025, of the 8 people that made a request through the largest assisted suicide association (DGHS) due to ME/CFS, 5 were between 24 and 29 years old. There are sadly no official numbers for total assisted suicides due to ME/CFS (or any other reason) available.
Looking at a statistic I found, in 2024 the same association helped just 4 people in the same age range request assisted suicide:

Which you can also tell by the shadows making no fucking sense
It’s not prudish but still very virtuous from the one in chastity. So much so that they should receive constant affirmations of how good they are.
You can tell how adept I am at choosing names by looking at my Lemmy user name. Numbers is all I’ve got!
And like a real gang, everything boils down to you doing all the work while they just sit and listen >:(
Goddammit plushie #31, why can’t YOU do the dishes for once??
https://grapheneos.org/releases#2026090700
All of the Android 17 security patches from the current September 2026, October 2026, November 2026, December 2026, January 2027, February 2027 and March 2027 Android Security Bulletins are included in the 2026090701 security preview release. List of additional fixed CVEs:
- Critical: CVE-2026-28591, CVE-2026-28604, CVE-2026-28639, CVE-2026-28653, CVE-2026-28662, CVE-2026-28666, CVE-2026-45515, CVE-2026-45531, CVE-2026-49879, CVE-2026-49882, CVE-2026-49884, CVE-2026-49918, CVE-2026-49921, CVE-2026-49926, CVE-2026-49927, CVE-2026-49932, CVE-2026-49933, CVE-2026-55256, CVE-2026-55265, CVE-2026-55268, CVE-2026-55269, CVE-2026-55273, CVE-2026-55277, CVE-2026-55280, CVE-2026-58814, CVE-2026-58820, CVE-2026-58823, CVE-2026-58835, CVE-2026-58865, CVE-2026-58868, CVE-2026-58876, CVE-2026-58880, CVE-2026-58882, CVE-2026-58984
- High: CVE-2025-22424, CVE-2025-22426, CVE-2025-22442, CVE-2025-48564, CVE-2025-48565, CVE-2025-48566, CVE-2025-48600, CVE-2026-0053, CVE-2026-28581, CVE-2026-28582, CVE-2026-28584, CVE-2026-28588, CVE-2026-28593, CVE-2026-28594, CVE-2026-28599, CVE-2026-28600, CVE-2026-28602, CVE-2026-28603, CVE-2026-28606, CVE-2026-28607, CVE-2026-28612, CVE-2026-28613, CVE-2026-28614, CVE-2026-28617, CVE-2026-28619, CVE-2026-28620, CVE-2026-28622, CVE-2026-28623, CVE-2026-28624, CVE-2026-28626, CVE-2026-28627, CVE-2026-28630, CVE-2026-28631, CVE-2026-28633, CVE-2026-28634, CVE-2026-28635, CVE-2026-28638, CVE-2026-28643, CVE-2026-28645, CVE-2026-28650, CVE-2026-28652, CVE-2026-28655, CVE-2026-28657, CVE-2026-28658, CVE-2026-28660, CVE-2026-28663, CVE-2026-28664, CVE-2026-28665, CVE-2026-28667, CVE-2026-28668, CVE-2026-28671, CVE-2026-45513, CVE-2026-45514, CVE-2026-45517, CVE-2026-45518, CVE-2026-45519, CVE-2026-45520, CVE-2026-45521, CVE-2026-45522, CVE-2026-45523, CVE-2026-45524, CVE-2026-45525, CVE-2026-45527, CVE-2026-45528, CVE-2026-45529, CVE-2026-49878, CVE-2026-49880, CVE-2026-49881, CVE-2026-49885, CVE-2026-49887, CVE-2026-49895, CVE-2026-49896, CVE-2026-49912, CVE-2026-49913, CVE-2026-49914, CVE-2026-49923, CVE-2026-49924, CVE-2026-49925, CVE-2026-49931, CVE-2026-49934, CVE-2026-49935, CVE-2026-49937, CVE-2026-55257, CVE-2026-55260, CVE-2026-55261, CVE-2026-55262, CVE-2026-55263, CVE-2026-55264, CVE-2026-55266, CVE-2026-55270, CVE-2026-55271, CVE-2026-55272, CVE-2026-55274, CVE-2026-55278, CVE-2026-55279, CVE-2026-55282, CVE-2026-55284, CVE-2026-55286, CVE-2026-55287, CVE-2026-55288, CVE-2026-55289, CVE-2026-55290, CVE-2026-55292, CVE-2026-55294, CVE-2026-58815, CVE-2026-58817, CVE-2026-58821, CVE-2026-58822, CVE-2026-58834, CVE-2026-58836, CVE-2026-58837, CVE-2026-58838, CVE-2026-58841, CVE-2026-58853, CVE-2026-58854, CVE-2026-58856, CVE-2026-58857, CVE-2026-58859, CVE-2026-58866, CVE-2026-58867, CVE-2026-58868, CVE-2026-58869, CVE-2026-58870, CVE-2026-58871, CVE-2026-58872, CVE-2026-58875, CVE-2026-58877, CVE-2026-58879, CVE-2026-58883, CVE-2026-58884, CVE-2026-58885, CVE-2026-58886, CVE-2026-58933, CVE-2026-58934, CVE-2026-58935, CVE-2026-58937, CVE-2026-58938, CVE-2026-58943, CVE-2026-58944, CVE-2026-58945, CVE-2026-58946, CVE-2026-58949, CVE-2026-58951, CVE-2026-58953, CVE-2026-58954, CVE-2026-58955, CVE-2026-58956, CVE-2026-58957, CVE-2026-58958, CVE-2026-58960, CVE-2026-58961, CVE-2026-58962, CVE-2026-58963, CVE-2026-58964, CVE-2026-58965, CVE-2026-58966, CVE-2026-58968, CVE-2026-58969, CVE-2026-58970, CVE-2026-58971, CVE-2026-58972, CVE-2026-58973, CVE-2026-58974, CVE-2026-58975, CVE-2026-58976, CVE-2026-58978, CVE-2026-58979, CVE-2026-58985, CVE-2026-58986, CVE-2026-58988, CVE-2026-58990, CVE-2026-58993, CVE-2026-58994, CVE-2026-58995, CVE-2026-58997, CVE-2026-58998, CVE-2026-59000, CVE-2026-59001, CVE-2026-59002, CVE-2026-59003, CVE-2026-59004, CVE-2026-59005, CVE-2026-59006, CVE-2026-59007, CVE-2026-59008, CVE-2026-59011, CVE-2026-59013, CVE-2026-59014, CVE-2026-59015, CVE-2026-59016, CVE-2026-59017, CVE-2026-59020, CVE-2026-59021, CVE-2026-59022, CVE-2026-59023, CVE-2026-59028, CVE-2026-59032
- Unclassified: CVE-2026-58994
Use ellipse select tool with a fixed aspect ratio of 1:1. Then Select -> Border and choose a width. Then fill it with a color.
Like yeah, it is 3 steps instead of having a dedicated “Shapes” tool with a bunch of options that would do the same. But GIMP is kind of built around selections, you do need to learn to use them if you ever want to use GIMP effectively. It’s about as important as understanding layers.
Nah, they’re great. I’ve had to pick up bottle caps because they slipped out of my hand before.
It’s genuinely more convenient imo to have the caps attached to the bottle.
Has the US ever done so? I don’t think that’s a real risk. Or rather, it’s not any higher than the US threatening to nuke Italy unless the organization is disbanded.
Not quite, this does have certain legal implications. Check out the CC0 license’s “Public License Fallback” text: https://creativecommons.org/publicdomain/zero/1.0/legalcode.en#fallback
The “license to do whatever” is more like a “license to do whatever except for whatever a court ruled I cannot give a license for”.
Public domain is a thing in the EU but not releasing anything into public domain.
In Germany, I cannot renounce my copyright to anything. I can give you an indefinite, unrestricted license to do whatever but I still own the copyright. It will only ever become public domain 70 years after my death, not a day sooner or later.
The US is literally worse than the entire EU despite having fewer inhabitants lmao
https://www.statista.com/statistics/191137/reported-forcible-rape-cases-in-the-usa-since-1990/
In 2024, there were 127,527 reported rape cases in the United States
https://www.statista.com/statistics/1072770/number-of-rapes-in-europe/
France: 42,000
Germany: 13,000
Sweden: 9000
Spain: 4500
Rest combined: <30,000 (roughly estimated by me)
Edit: The statistic does not include all EU nations. Italy, Belgium and the Netherlands are the largest one’s missing from what I can see.
The EU has 100,000,000 more inhabitants by the way.
Also most rapes are domestic. That’s also the primary reason for the lack of reports - people do not want their marriage to end, their families/friends to turn their backs etc. What use is a gun here?

Like this:

Adjust the distance between the left and right ball earmuff and you get an (admittedly large and spiky) non-erect cock.
Maybe I’m being rohrschached but the first thing the new logo reminds me of is cock and balls. In an abstract way.
Hybride Angriffe werden ja durch Wegwerfagenten verursacht. Also “Angriffe as a service”. Dass der Service-“Mitarbeiter” entsprechend wenig involviert in der Planung ist und vermutlich keine Qualifikationen (wie z.B. Erfahrung im Bau von Brandsätzen) hat ist nicht wirklich verwunderlich.





Germany’s app (AusweisApp2) is open source and available for literally every platform. Linux, FreeBSD and even Fdroid included.
I’m not sure of the exact functionality and whether the government can track anything. You need to scan your ID, the app will then ask for a PIN (2fa) and then will tell you which data will be sent to whoever made the request.
Authentication is done through an eID server which in theory anyone can set up. The requirement are quite strict though so right now there are only three providers. They check the validity of the ID and request and send the received ID data to the requestor.
It’s quite the complicated procedure to ensure the highest possible security and privacy.
The entire process is publicly documented and you can probably spend a few hours trying to understand it.
As for locking people out of online communities: I don’t think it’s a problem if and only if the legislation applies exclusively to social media providers above a certain size. Such as having 5 million+ monthly users.